Relution Server 26.5
Important note regarding the update: If you are currently using an older version, we recommend that you first update to version 26.0.3 and then to version 26.5.
Meta-organisations for enhanced client management
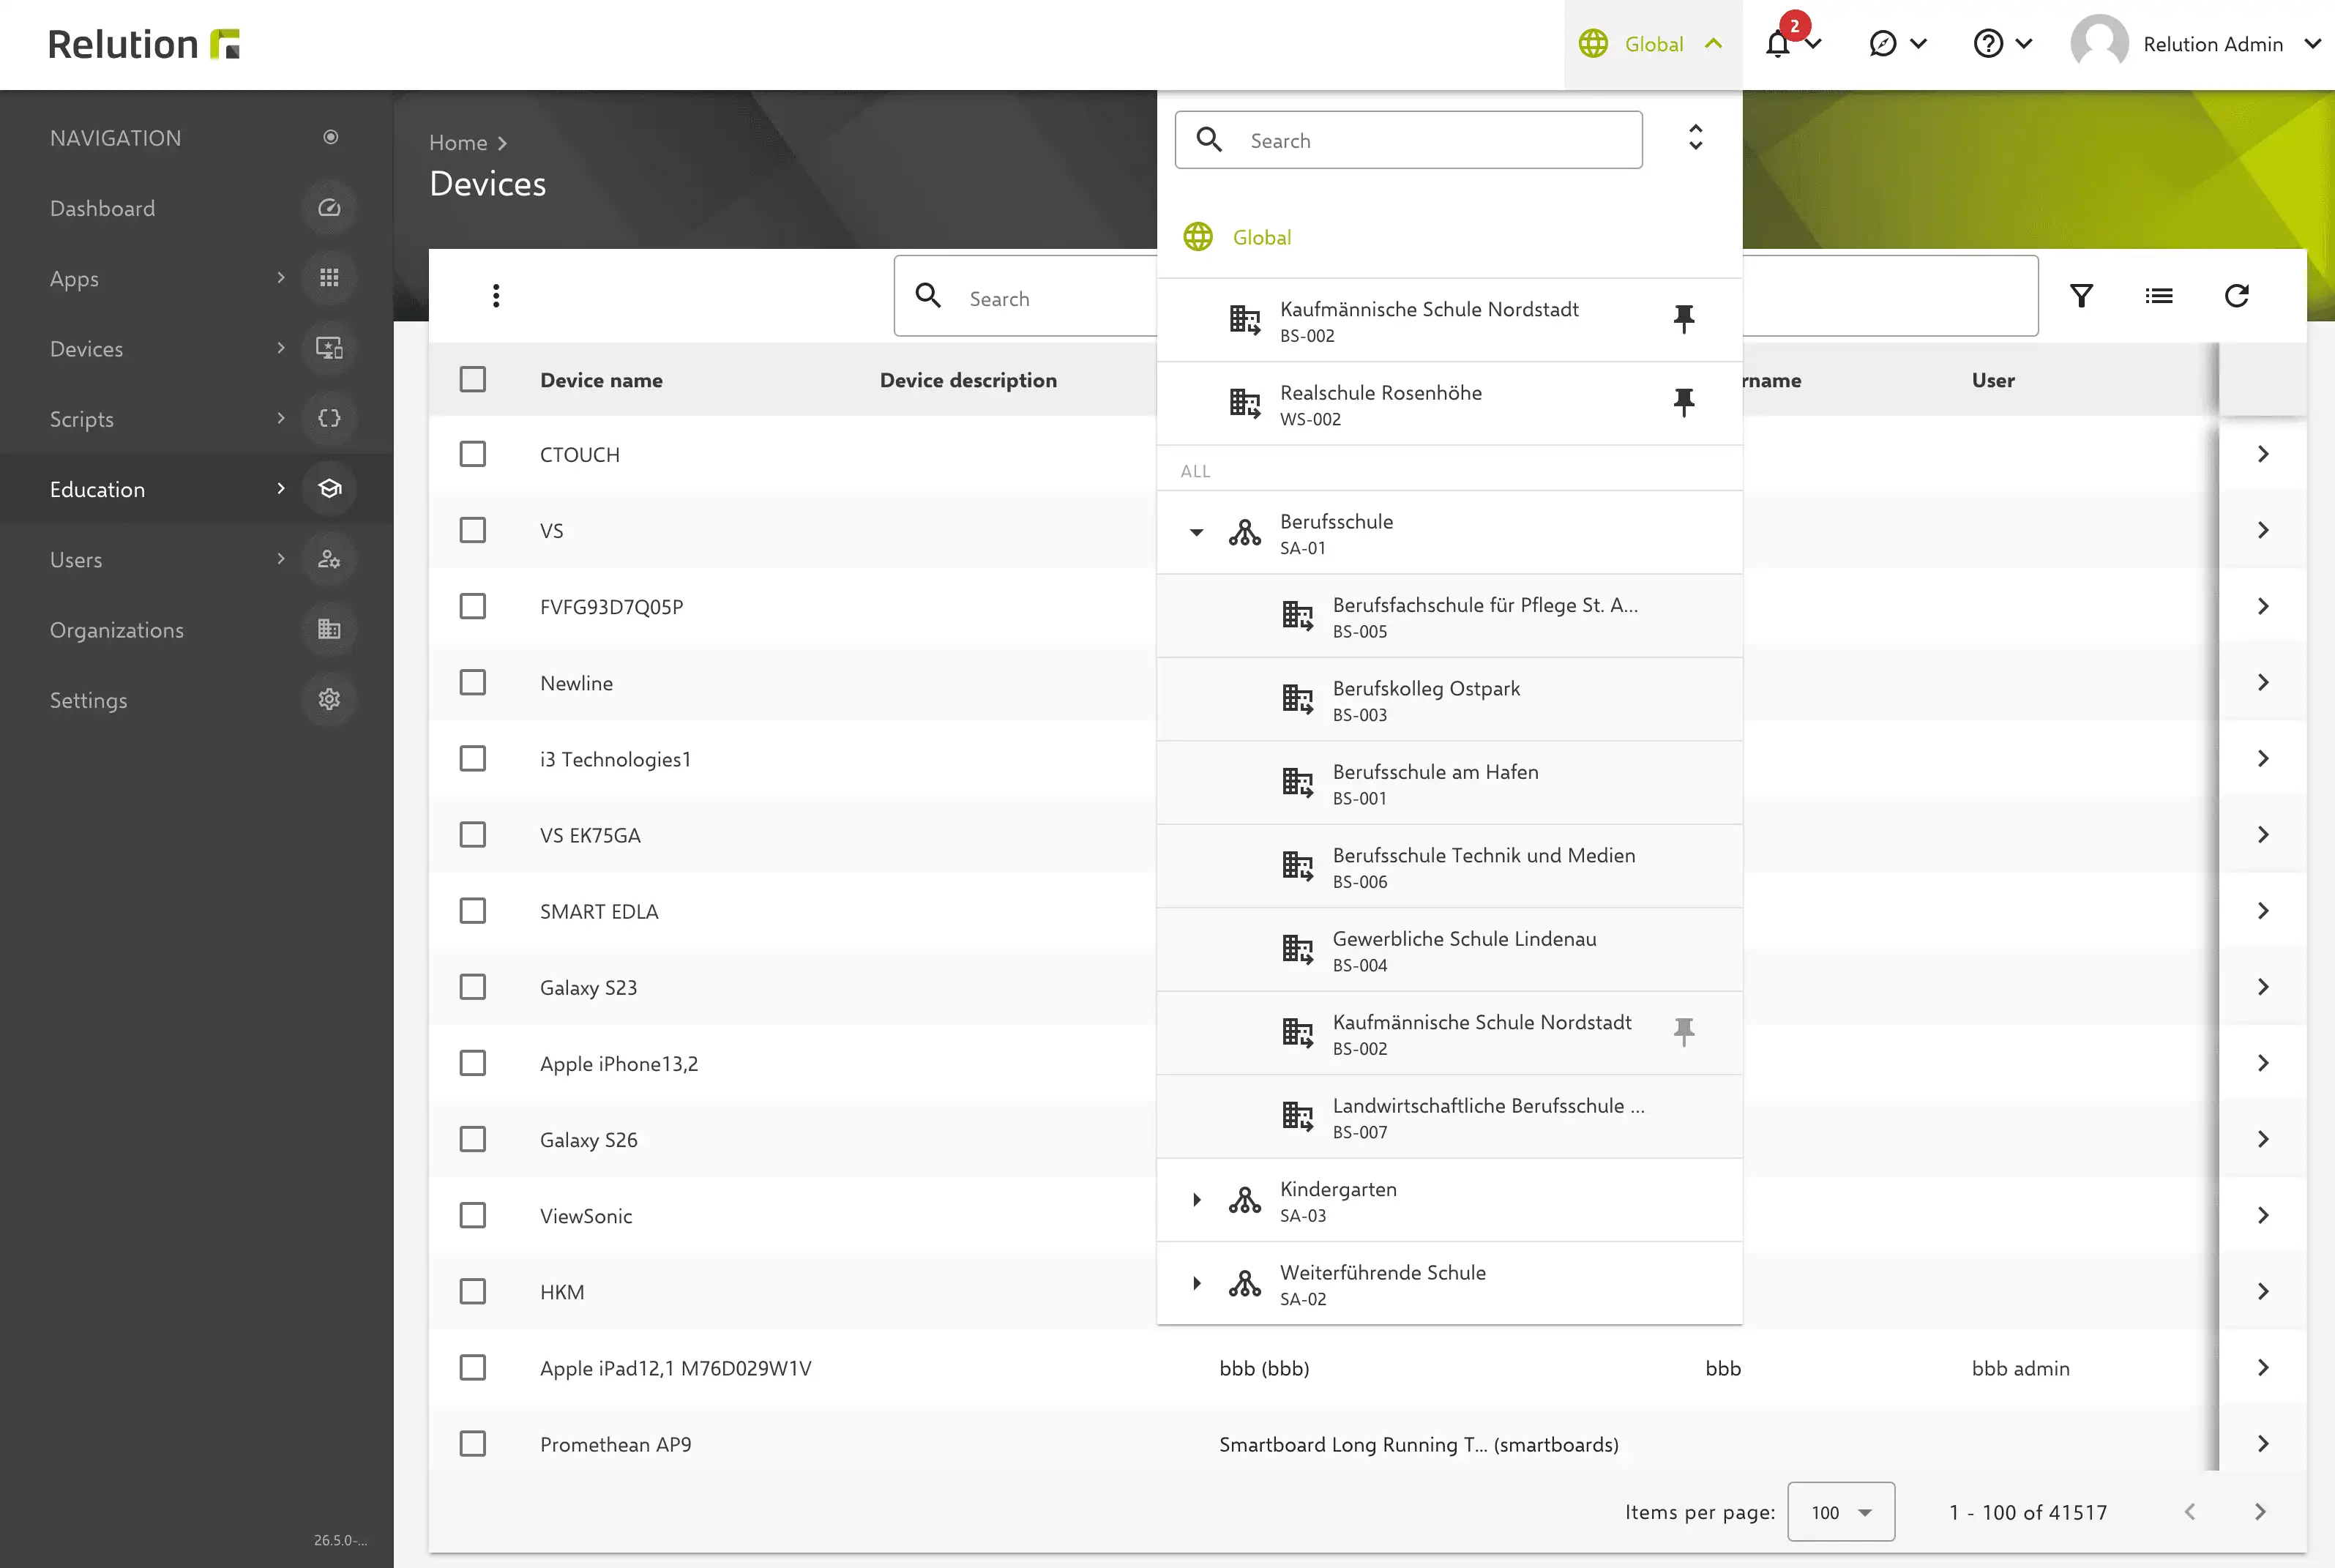
With the new meta-organisations, Relution is introducing a higher-level structure for the centralised management of multiple Relution organisations (clients).
Meta-administrators can manage multiple sub-organisations as a group, centrally controlling policies, device groups, users and devices.
Existing Relution organisations can be assigned to a meta-organisation at a later date without having to be set up from scratch. Assigned sub-organisations are displayed indented in the organisation overview, so that the hierarchical structure is immediately apparent.
The new feature is particularly suitable for school authorities, corporate structures and other organisations with multiple independent units.
Key benefits
- Cross-organisation overview: Meta-administrators can view devices, users and groups across all associated sub-organisations centrally.
- Shared resources: Policies and device groups can be deployed centrally across multiple sub-organisations.
- Centralised app and licence management: Apps and app licences (VPP) can be managed centrally and distributed to sub-organisations.
- Automated user assignment: During synchronisation via LDAP, Microsoft Entra ID, SchulConnex or Apple School Manager, users can be automatically assigned to the appropriate sub-organisation.
- Centralised administration: Scripts, permission roles, default administrators and auto-enrolments can be managed centrally across the organisation.
- Secure organisational structure: Assigned sub-organisations are protected against accidental deletion.
Setting up the organisational structure
When creating a new organisation, there are now three options available for the organisation type:
- Stand-alone: As before, the organisation is created directly under the global organisation and managed independently of other organisations.
- Meta-organisation: The organisation acts as a parent organisation and can manage several sub-organisations.
- Sub-organisation: The organisation is assigned to an existing meta-organisation. To do this, the desired meta-organisation must be selected.

Relution can be used as an Identity Provider (IdP)
With Relution 26.5, Relution can be used as an Identity Provider (IdP). An Identity Provider (IdP) handles the central management and verification of user identities and enables users to log in to multiple connected applications using a single existing account.
This allows external applications and services to be integrated via Relution using Single Sign-On (SSO). Users log in with their existing Relution account and do not need to log in separately for each application. This simplifies the central management of integrated applications, whilst users benefit from a consistent login process. The OpenID Connect (OIDC) and SAML standards are supported.
Applications can be registered and managed as clients, including dynamic registration and public clients without a client secret. A new consent page provides information about the access rights requested, which users can then view and revoke. In addition, session management, automatic JWK key rotation and extended logging of logins and applications used are available.
Note: This feature is currently in the beta phase. We’d love for you to test it and provide feedback on your experience.
(New) Dashboard for flexible, customised analytics
The dashboard in Relution has been completely revamped and now offers administrators significantly more options for customising and analysing information. Every organisation can now have its own dashboard. Various widgets can be created, configured and added to as required. The size and position of the widgets can also be flexibly adjusted – this applies across all organisations.
In addition, custom filters allow you to narrow down the data displayed – for example, to specific devices or users.
User profile with tab-based structure
In version 26.5, the profile view features a clearer layout and a revamped, tab-based design. This means that the various pieces of information are more clearly structured and quicker to access.
User data can be edited directly, whilst additional information such as organisation, external ID and identity provider is clearly organised in separate tabs.
Enhanced permissions management for device group actions
Permissions for actions on device groups have been expanded. Administrators can now specify more precisely which actions may be carried out on device groups.
This allows, for example, deletion actions on device groups to be prevented if an administrator does not have the necessary permission in the inventory.
Optimised certificate management
Certificate management in Relution is being enhanced with several new features in version 26.5. With the new certificate pool, existing certificates can be imported into Relution as a collection and made available centrally. This means that this option is also available to customers who are unable to connect their own external PKI to Relution. Otherwise, there is no way to transfer certificates from a PKI to an MDM. Certificate templates and Relution’s own certificates can still be used as usual.
Furthermore, it is now possible to store multiple user certificates of the same type and uniquely identify them by name and type. The stored certificates can then be used as usual in certificate configurations.
Certificates can also be embedded directly into configurations using Base64-encoded placeholders, for example for managed apps.
Rootless Docker: Greater security for the Relution Server
The Relution Server now runs as a rootless Docker container by default. To achieve this, the Docker image uses a built-in Relution user, meaning the container no longer needs to be run with root privileges.
This makes running the Relution Server more secure and aligns with current best practices for operating Docker containers. Features that previously required root privileges have been adapted accordingly. These include, amongst other things, the management of additional CA certificates, which can now be configured directly via Relution.
S3 and resource storage optimisations
Storage management in Relution has been optimised for more efficient file processing. Uploads and resources are now stored more efficiently. This reduces the load on the database and improves the delivery of apps, background images and other resources.
Improvements to VPP management
The management of Apple VPP licences has been optimised in several areas. When devices are deleted, assigned app licences are now automatically released. At the same time, licence assignment has been stabilised to prevent duplicate assignments and unnecessary API calls to Apple.
Error handling during communication with Apple has also been improved. Issues with VPP notifications and DEP registration in certain configurations have been resolved.
Certificate pinning for Apple enrolment profiles
Relution version 26.5 supports certificate pinning for Apple enrolment profiles. This allows administrators to specify which certificates are trusted for encrypted MDM communication.
Certificate verification can thus be restricted specifically to the certificates stored in the enrolment profile. This enhances the security of device communication and protects the enrolment process from unwanted or tampered certificate chains.
Managed Software Updates for Apple Devices
With the new ‘Managed Software Updates’ configuration, administrators can specify a desired operating system version and a local time for enforcing the update on Apple devices. The settings are implemented via Apple’s Declarative Device Management (DDM).
Specifying the minimum OS version for Apple DEP enrolments
For the DEP enrolment of Apple devices (iOS, macOS, visionOS), a minimum operating system version can now be specified in Relution. Devices running a version lower than this will initially be prompted by the system wizard to update. Only once the software version has been reached will enrolment continue and the management profile be deployed. It is possible to specify whether devices that can no longer meet the minimum version requirement are permitted to enrol.
Relution Decon now also available for macOS
Relution Decon is now also available for macOS. With Relution Decon, content filtering on macOS can be configured and managed centrally via Relution. Policies can be set centrally via the Relution platform and enforced consistently across devices.
Autofill feature can be controlled on Android Enterprise devices
For Android Enterprise, it is now possible to set a default for autofill behaviour via restrictions. This allows administrators to specifically enable or restrict the system-wide autofill feature on managed devices.
New design for the Teacher App
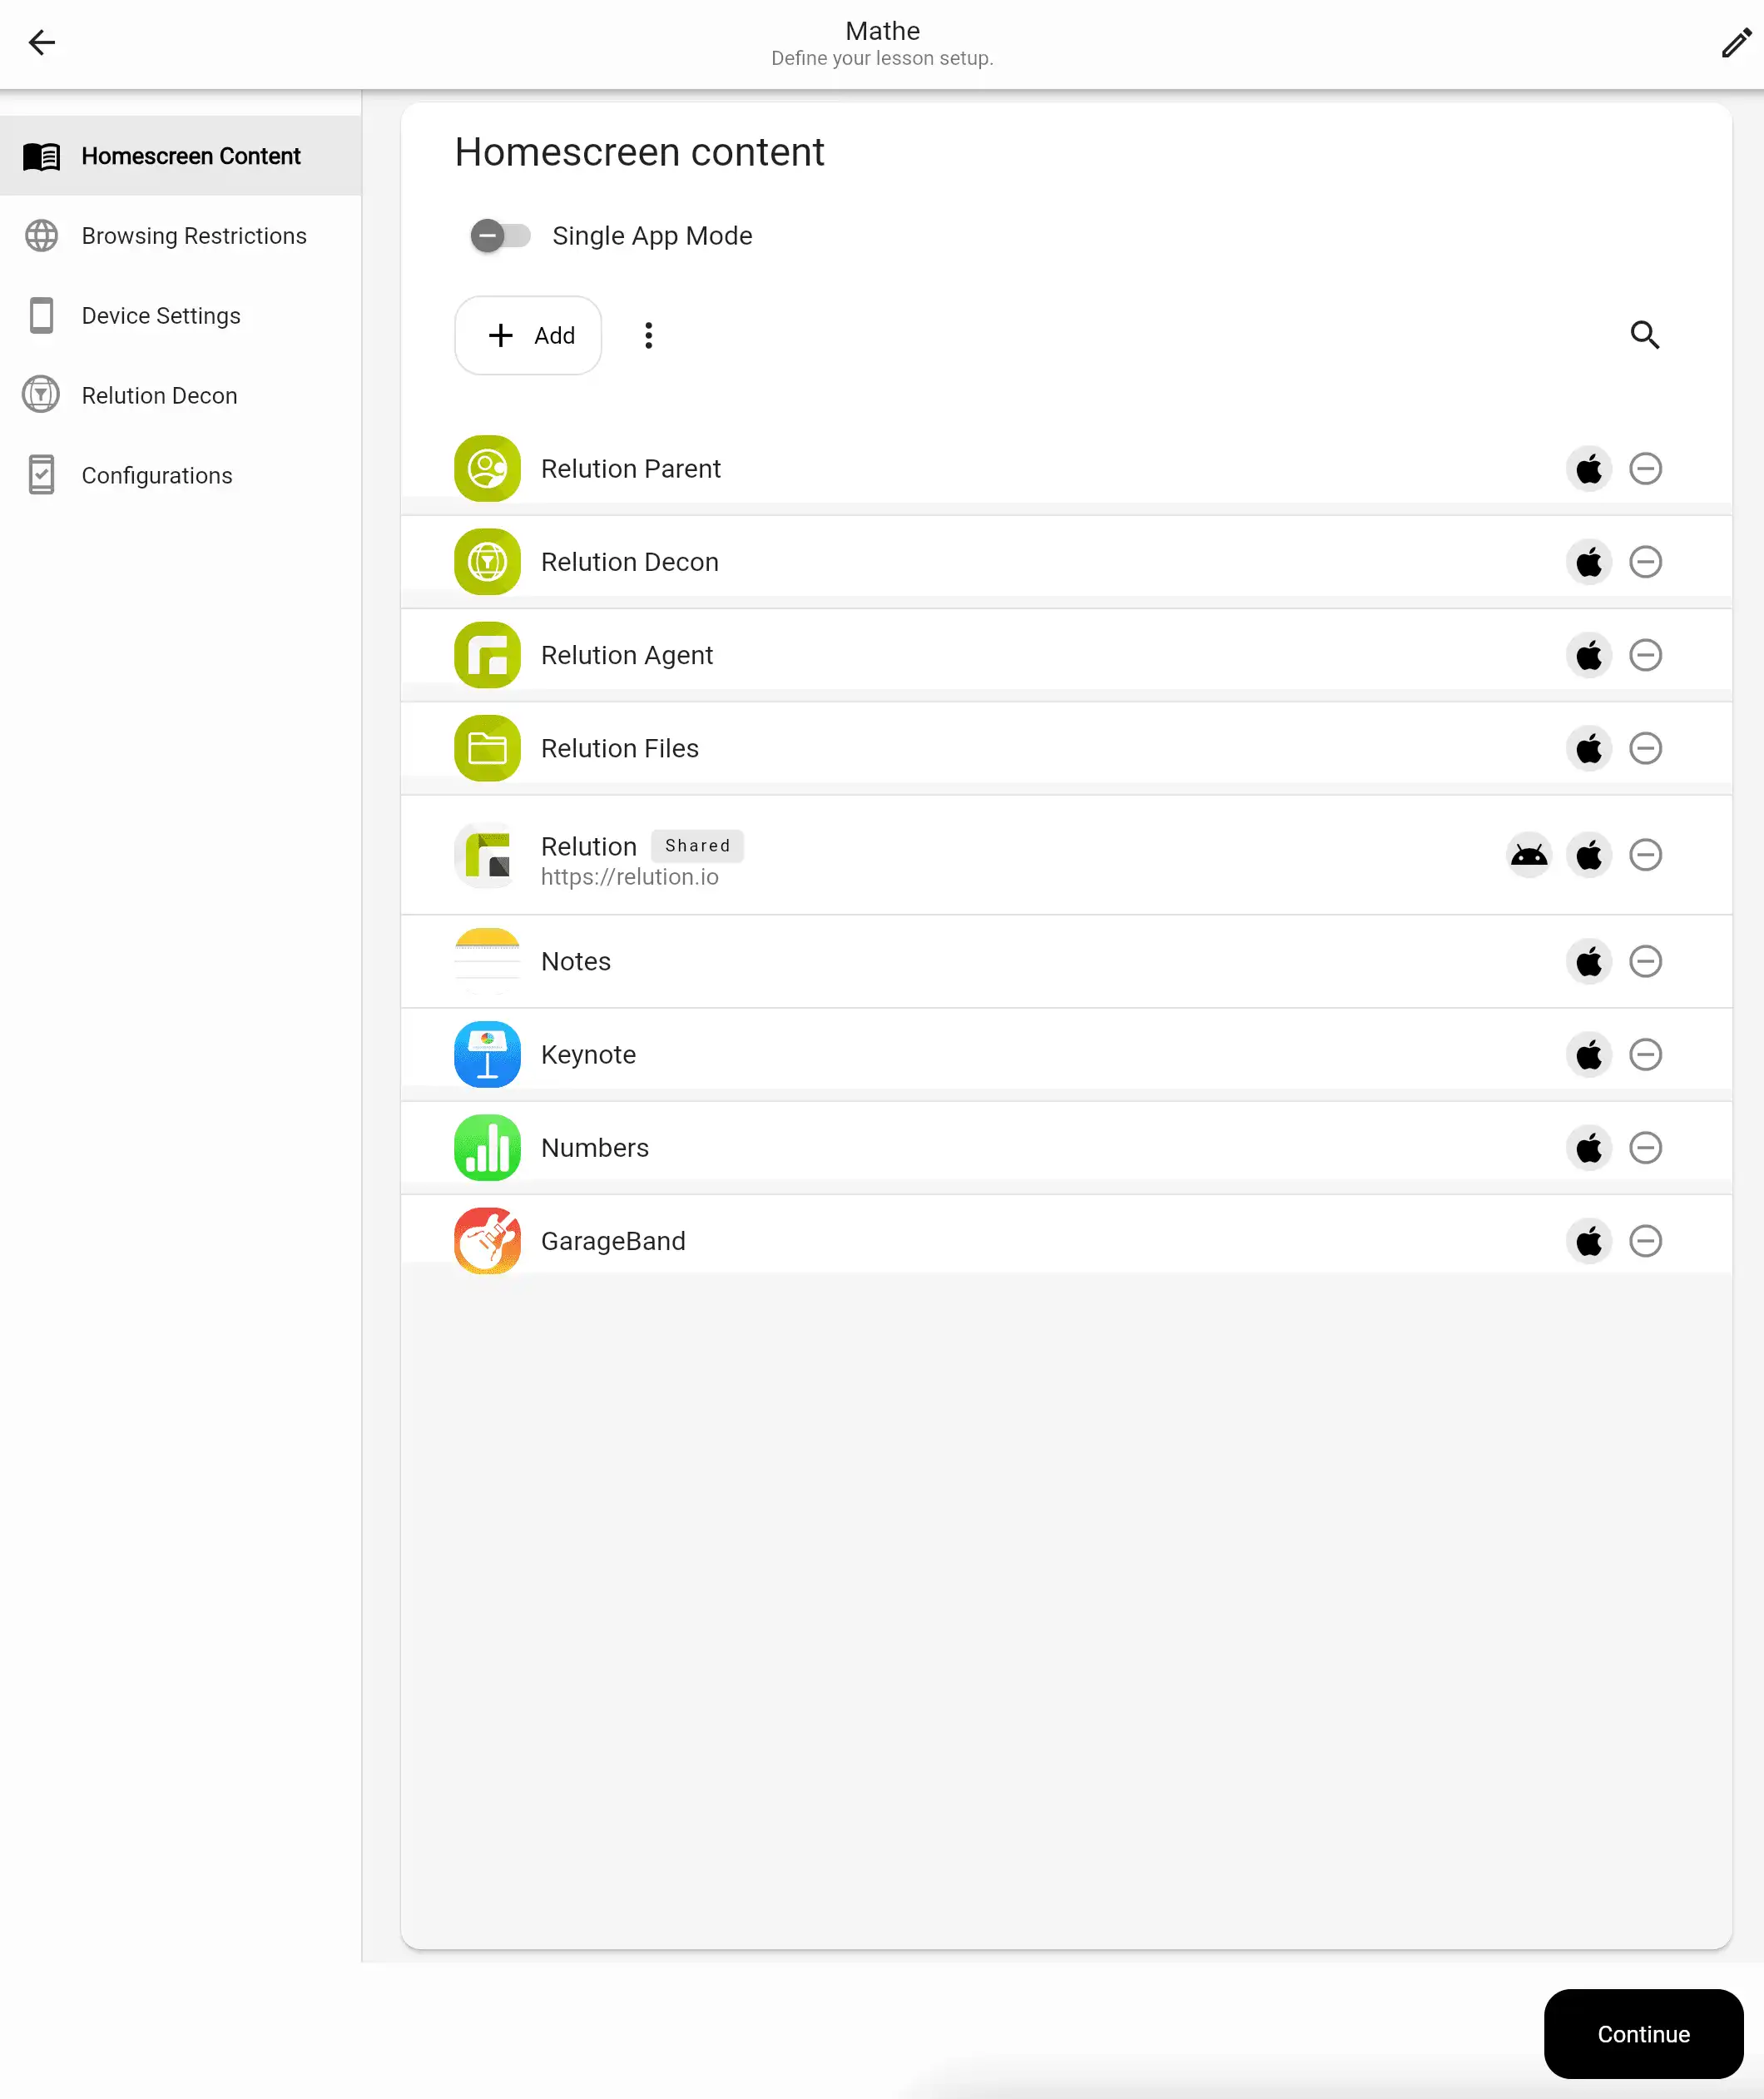
The Relution Teacher App now features a revamped user interface. Version 26.5 makes it possible to link lesson templates to pre-defined configurations. Teachers can assign configurations approved by the administrator directly to a lesson.
At the start of the lesson, the stored policies are automatically applied to the participating pupils’ devices and removed again once the lesson has ended. This allows device settings to be controlled specifically for individual teaching situations.
In addition, the process for creating lesson templates has been revamped; they can now be created via a clear, two-step process with sidebar navigation. Templates can also be created without device configuration, meaning that no additional restrictions apply to pupils’ devices.
For the new web browsing restrictions, bookmarks, additional permitted URLs and lists of websites via CSV import are available. Administrators can also specify which configurations are available to teachers and who is permitted to use the feature.

You can find the changelog for this release here.
For the sake of readability, the masculine form is used on this page for personal pronouns and personal nouns. In the interests of equality, these terms apply to all genders. The use of the masculine form is for editorial reasons only and does not imply any judgement.